Key takeaways
- An SSL certificate is a data file on your web server that
- The TLS handshake is the exchange that sets up that encrypted connection — it happens in milliseconds, before any page content loads.
- A certificate authority issues and digitally signs your certificate. Browsers trust it because they trust the authority.
- Certificates don't last long, and they're getting shorter: maximum validity drops to 200 days in March 2026 and 47 days by 2029.
An SSL (Secure Sockets Layer) certificate is a security technology that creates an encrypted connection between a web server and a browser. This ensures that the data passing between them stays private and can’t be tampered with. It also verifies to site visitors that they’ve reached the correct, genuine website that they intended to visit.
Although SSL was replaced by TLS (Transport Layer Security) many years ago, SSL remains the common name for the technology. Its main use is but the same protocol also protects email, VoIP, and other traffic over untrusted networks.
This guide covers exactly how that secure connection is established, what’s inside a certificate, who decides which certificates browsers trust, and how long certificates last.
Use this free website security checker to review how well your website protects visitors.
What is an SSL certificate?
An SSL (Secure Sockets Layer) certificate is a small data file installed on a web server. It holds the public key that helps make encryption possible and carries certificate information digitally signed by the Certificate Authority. Depending on the validation level, the certificate may also include verified information about the organization operating the site.
For a more in-depth look, check out our ultimate guide to SSL certificates.
What’s the difference between HTTP and HTTPS?
HTTP and HTTPS aren’t separate protocols. HTTPS is when HTTP is running inside an encrypted TLS connection. The SSL certificate is what makes that encrypted connection possible.
With an SSL certificate properly installed on a web server, your website is able to be reached via https://. Without it, you’re limited to http:// only, and your site will be labeled as Not Secure.
Check out this guide on how to protect user data for more information.
SSL vs TLS: What’s the difference?
SSL and TLS are both protocols for securing data as it travels between a browser and a website. SSL came first, developed by Netscape in 1995. TLS replaced it in 1999 as its standardized successor.
Why does this distinction matter? Because SSL isn’t just an older version of TLS; it’s a completely separate, retired protocol. SSL 2.0 and SSL 3.0 have known, unfixable vulnerabilities and are now prohibited. No current browser or server will negotiate an SSL connection.
What’s actually in use today is TLS 1.2 and TLS 1.3. TLS 1.3, finalized in 2018, is the current standard. Old cipher suites were removed, forward secrecy became mandatory, and handshakes were cut down to a single round trip, making secure connections faster than earlier versions.
When you buy an SSL certificate, you’re actually buying a certificate used by TLS. The SSL certificate name has stuck around because it entered common use first, so you’ll see the term still in use by certificate companies, hosting providers, and browsers.
If you’re configuring a server, you’ll want to select support for TLS 1.2 and 1.3, disable SSL 2.0, SSL 3.0, TLS 1.0, and TLS 1.1. Most hosting platforms do this by default currently, but it’s a good idea to confirm what your particular configuration offers with GoDaddy’s SSL configuration test.
How does SSL work?
SSL creates an encrypted connection between a browser and a server so information can move safely across the internet. The process relies on a combination of authentication, encryption, and integrity checks that work together every time someone visits your site.
SSL does three things, and each process below exists to deliver one of them:
- Encryption: scrambles data in transit so anyone intercepting it reads nothing usable.
- Authentication: proves the server is who it claims to be, so you're not handing data to an impostor.
- Integrity: detects any alteration in transit, so the data arriving is the data that was sent.
These three functions work tightly together to prevent eavesdropping on traffic, tampering with traffic, and helps protect visitors from connecting to an unauthorized server impersonating the certified domain. It’s nearly impossible for encryption to work without the other two parts, since a perfectly encrypted connection to an attacker’s server is still a connection.
Encryption isn’t the hard part; providing identity is.
It’s important to note that the certificate itself doesn’t provide encryption. An SSL certificate supplies the verified identity that makes encryption meaningful.
The sections below walk through the major components that make SSL work, so you can choose the best SSL setup for your site.
The SSL/TLS handshake: Step-by-step breakdown
The TLS handshake using an SSL certificate is the first step in creating a secure web session. It sets the rules for the connection before any data is exchanged. Although it happens very quickly, it includes several important stages that determine how the browser and server communicate safely.
- The browser reaches out to the server. It requests a secure session and shares information about what encryption methods it supports.
- The server responds with its SSL certificate. This certificate contains the public key and the details needed to identify the website.
- The browser checks the certificate. It verifies that the certificate is valid, trusted, and issued to the correct domain.
- Both sides agree on encryption settings. They choose the strongest encryption method supported by both the browser and the server.
- A session key is created. This key is generated for the specific session and is used to encrypt all data during the visit.
- Secure communication begins. Once the session key is in place, the browser and server switch to encrypted data transfer.
None of this process is visible to visitors. From their point of view, they click a link, their browser requests the certificate, verifies it, negotiates a cipher, and establishes a session key — all within a few hundredths of a second.
If your certificate isn’t installed correctly (or at all), the visitor will see an error and a missing https:// in the web address. A misconfigured certificate is the only time that this handshake process becomes visible and can lead to a loss of trust for your site. Reliable SSL certificates help ensure this handshake works as intended for every visitor.
What’s different in TLS 1.3
Older TLS versions needed two round trips between browser and server to complete the handshake. TLS 1.3 reduced this to one, measurably shortening the delay before a page starts loading, making modern TLS connections faster than the unencrypted HTTP connection it replaced on many sites. It also removed the weaker cipher suites earlier versions permitted, so there are fewer ways to configure it insecurely.
Looking further ahead, the public key algorithms underpinning TLS today are expected to become vulnerable to quantum computing, which is why the industry is beginning a transition to post-quantum cryptography. See what website owners should know about PQC certificates.
What are public, private, and session keys?
SSL uses three keys, and the difference between them is what makes the whole system work. This is an application of public key cryptography, and certificates are one component of a wider system called public key infrastructure (PKI).
The public key lives inside your certificate and is handed to every visitor who connects. It can encrypt data, but it can't decrypt it. The private key stays on your server and is never transmitted. It's the only thing that can decrypt what the public key encrypted, which is how a browser knows it's talking to the real server and not an impersonator. Lose control of your private key and the certificate must be reissued.
Asymmetric encryption during the handshake
Asymmetric encryption is used during the handshake. It involves a pair of keys, one public and one private, that work together to create the session key. Only the server has the private key, which allows the connection to remain protected.
Symmetric encryption after the handshake
Symmetric encryption is used after the handshake. This method uses the shared session key to encrypt and decrypt all data. It keeps the connection fast while still maintaining high levels of security.
Why should both be used? Because while asymmetric encryption is slow and symmetric encryption is fast, both sides are required in order to share a key. The handshake process uses the slow method once to agree on a shared key safely, then switches to the faster method for everything after.
How does SSL encrypt data?
Encryption is the core function of SSL. It keeps information from being read by anyone who intercepts it. Combined, the two methods above keep user information private while it is transmitted throughout the entire web session. To dig deeper, see our guide to data encryption.
How does SSL verify a website’s identity?
Authentication protects users from fake or impersonated websites. When a browser connects to a server, it must confirm that the website is legitimate. This verification happens through the SSL certificate. The browser reviews:
- The Certificate Authority (CA) that issued the certificate
- The validity dates
- The domain for which the certificate was issued
- Whether the certificate has been revoked
If everything checks out, the browser knows it is communicating with the real site. This protects users from attackers who might try to imitate a trusted website to capture sensitive information.
How does SSL prevent data tampering?
Data integrity ensures information stays accurate while it travels between a browser and a server. TLS protects each record with cryptographic integrity checks. Older cipher suites use a separate message authentication code (MAC), while modern TLS deployments commonly use authenticated encryption (AEAD) cipher suites, where integrity is provided by an authentication tag built into the encryption. These tools help the browser confirm that:
- The data received is the same data the server sent
- No one modified or replaced the information
- The session has not been hijacked or altered
If a mismatch is detected, the browser can stop the connection immediately to prevent further issues. This protects both the user and the business.
Let's help you find the right SSL certificate to help you protect your site.
How long do SSL certificates last?
Every certificate has a validity period, which is a fixed window during which browsers will trust it. Once it lapses, browsers show a full-page security warning instead of your site, and most visitors won't click through. Certificates don't renew themselves unless you've set that up.
Note: GoDaddy Deluxe Automated SSL and Managed SSL Service automate re-installation as certificate validity periods expire.
Recent changes to validity periods by the CA/Browser Forum are important to note, as they’ve shrunk the validity periods significantly.
| Certificates issued on or after | Maximum validity | Maximum domain validation reuse |
|---|---|---|
| March 15, 2026 | 200 days | 200 days |
| March 15, 2027 | 100 days | 100 days |
| March 15, 2029 | 47 days | 10 days |
The reasoning behind the change is risk exposure. If a private key is compromised, a short-lived certificate limits how long an attacker can exploit it. Revocation checking has never worked reliably, so the industry is reducing the window instead.
The practical effect ultimately lands on site owners. By 2029, SSL certificates will need to be reinstalled up to 12 times per year, but automation handles it so that you don’t have to.
Note that validity isn't the same as your subscription: a multi-year subscription still issues certificates in short validity blocks, each of which must be reinstalled. More on validity vs. subscription periods here.
How to tell if a site is using SSL
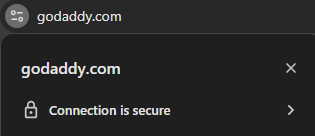
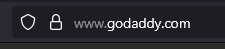
Most browsers give clear visual signs when SSL is active. On some browsers, like Firefox, you’ll see a padlock icon near the address bar, and the URL will begin with https instead of http. On Chrome, select the site information icon to the left of the web address to view the connection’s security status. For example:
| Browser | What you'll see |
|---|---|
| Chrome/Edge | A neutral site settings icon (two sliders) left of the URL — no padlock since Chrome 117. Click it, then Connection is secure to inspect the certificate. |
| Firefox | A padlock icon near the address bar. |
| Safari | A padlock; click the domain name for details. |
Common SSL problems
Even after installing an SSL certificate, you may still see a “Not secure” warning if something in the setup is incomplete. Issues can appear when redirects are not configured, mixed content is present, or the certificate was installed incorrectly. These situations are among the most common SSL errors site owners encounter. If you want help avoiding these problems, a managed SSL service can handle installation and ongoing maintenance for you.
All three are configuration issues rather than problems with the certificate itself, and all three are fixable. Our guide to adding an SSL certificate covers diagnosing and resolving each one, including the specific browser error codes you'll see. If you'd rather not handle it yourself, a managed SSL service can take care of installation and ongoing maintenance.
The ongoing importance of SSL for a safer web
SSL remains one of the most important tools for helping secure website connections and building trust with visitors. It helps protects data in transit, verifies site identity, and helps prevent common threats that target unencrypted connections. As online security needs continue to grow, keeping your SSL certificate active and properly installed is a key part of maintaining a safe experience for anyone who visits your site.
Certificate lifetimes are also getting shorter. Under a CA/Browser Forum–approved schedule, the maximum validity for publicly trusted TLS certificates drops from 398 days today to 200 days starting March 15, 2026, then 100 days on March 15, 2027, and 47 days on March 15, 2029 — making renewals (and ideally automation) more important than ever.
If you want a simple way to stay protected, explore GoDaddy’s SSL solutions and choose the option that fits your site’s needs.